CLUSTER HOST GATEWAY // SECURE
Booting (0%)
NODE: mac-client-uplinkLATENCY: 12msEST: 1.2S
Client Metrics
Live
Local CPU Est.
0.0%
JS Heap
0 MB
DEV/OPS
Harshit Boranaăƒăƒ«ă‚·ăƒƒăƒˆăƒ»ăƒœăƒ©ăƒŠ

DevOps Engineer

デブă‚Șプă‚čスンゾニケ
+
Scroll
PROFILE

About Me

私に぀いお / Profile

Hi there. I'm Harshit, a DevOps Engineer who loves to Build, Innovate, and Automate things. I focus on building robust, scalable infrastructure and seamless deployment pipelines.

When I'm not configuring servers or writing scripts, I'm usually exploring new tech or preparing for my next big challenge. Feel free to connect with me!
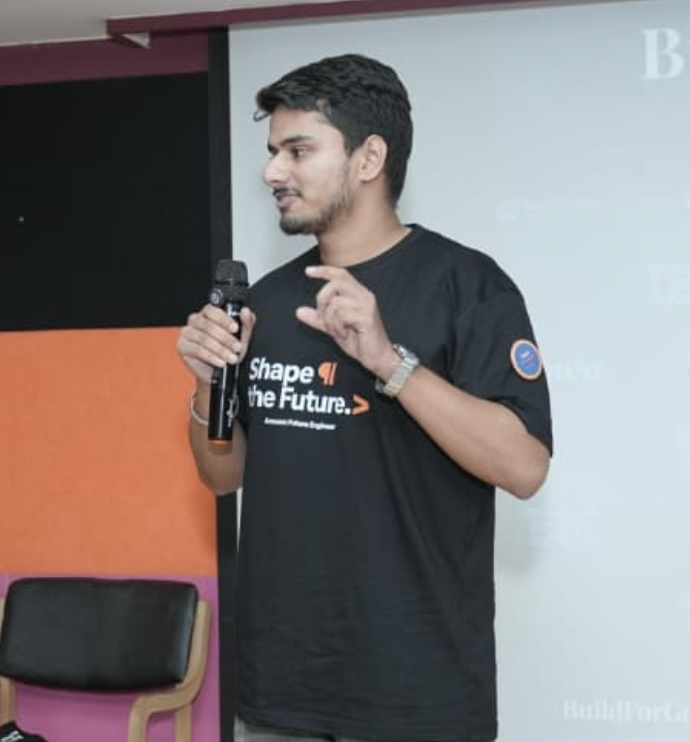
SPEAKERBuild Innovate Automate
Harshit Borana Portrait
ID: #HARSHIT-075
profile-specs.sh
HOST:Harshit Borana
ROLE:DevOps Engineer
LOC:Udaipur
SHELL:/bin/zsh
CORE:DevOps
UPTIME: 99.999%● STABLE

git log --oneline

Experience & Education History
commit a1b2c3dFeb 2026 - Present
Author: Harshit Borana <harshitborana2@gmail.com>

Trainee DevOps Engineer

Kadel Labs

Building CI/CD pipelines using GitLab CI/CD, Jenkins, and GitHub Actions. Managing applications on AWS (EC2, S3, IAM), containerizing builds with Docker, and monitoring infrastructure using Prometheus and Grafana.

commit f4e5d6cApril - July 2025
Author: Harshit Borana <harshitborana2@gmail.com>

DevOps Intern

Webanix Solutions

Designed robust CI/CD pipelines with Jenkins and Bitbucket. Containerized server setups on AWS EC2, configured NGINX reverse proxies for load balancing/SSL, and integrated AWS IoT Core MQTT communication.

プロゾェクト

Selected Works

Infrastructure & Code
01

Jenkins Shared Library Pipeline

ă‚Šă‚§ăƒ–ă‚·ă‚čテム / Web System
JenkinsGroovyKubernetesHelmCI/CDDocker

Enterprise-grade custom Jenkins Shared Library automating end-to-end CI/CD for multi-service microservices. Standardizes testing, security scanning, containerization, and canary Kubernetes deployments across all business units.

localhost:3000
pipeline-execution.logBUILD SUCCESSFUL
[Pipeline] Start Pipeline
[Pipeline] node (jenkins-agent-arm64)
[STAGE] Static Analysis
> Run SonarQube Scanner...
> Quality Gate Passed (0 errors)
[STAGE] Vulnerability Scan
> Trivy Scan container image...
> 0 Critical, 0 High Vulnerabilities
[STAGE] Build & Push
> Building container layers...
> Pushed to ecr.us-east-1.amazonaws.com
[STAGE] GitOps Sync
> Update Helm Tag to #1024
> ArgoCD Auto-Sync triggered successfully
[Pipeline] End: SUCCESS in 42s
infrastructure.yml
1// vars/microservicePipeline.groovy
2def call(Map config = [:]) {
3 pipeline {
4 agent { label 'docker-runner' }
5 options {
6 timeout(time: 1, unit: 'HOURS')
7 ansiColor('xterm')
8 disableConcurrentBuilds()
9 }
10 stages {
11 stage('Security Scan') {
12 steps {
13 sh "trivy image --severity HIGH,CRITICAL ${config.imageName}:${env.BUILD_ID}"
14 }
15 }
16 stage('Docker Build & Push') {
17 steps {
18 script {
19 docker.withRegistry("https://${config.registry}", 'ecr-credentials') {
20 def image = docker.build("${config.appName}:${env.BUILD_NUMBER}")
21 image.push()
22 }
23 }
24 }
25 }
26 stage('GitOps Sync') {
27 steps {
28 dir('gitops-manifests') {
29 git url: 'git@github.com:org/gitops.git', branch: 'main'
30 sh "kustomize edit set image ${config.appName}=${config.registry}/${config.appName}:${env.BUILD_NUMBER}"
31 sh "git commit -am 'infra: bump ${config.appName} to ${env.BUILD_NUMBER}' && git push"
32 }
33 }
34 }
35 }
36 }
37}
02

Multi-Cluster EKS GitOps Platform

ă‚Šă‚§ăƒ–ă‚·ă‚čテム / Web System
TerraformAWS EKSArgoCDPrometheusHelm

Automated provisioning of production-grade AWS EKS clusters using Terraform. Configured with ArgoCD for declarative GitOps continuous delivery, Prometheus/Grafana for monitoring, and External Secrets Operator.

localhost:3000
argocd-dashboard --app productionSynced
✓
eks-prod-clusterapplication.argoproj.io
argocd-ingress-gatewayService / Ingress
microservices-deploymentDeployment (3 Replicas)
pod/api-x82mpod/api-p01spod/api-q92k
infrastructure.yml
1module "eks" {
2 source = "terraform-aws-modules/eks/aws"
3 version = "~> 20.0"
4
5 cluster_name = "production-eks-cluster"
6 cluster_version = "1.29"
7
8 vpc_id = module.vpc.vpc_id
9 subnet_ids = module.vpc.private_subnets
10
11 eks_managed_node_groups = {
12 general = {
13 min_size = 3
14 max_size = 10
15 desired_size = 3
16 instance_types = ["t3.xlarge"]
17 }
18 }
19}
03

AWS Event-Driven Serverless Pipeline

ă‚Šă‚§ăƒ–ă‚·ă‚čテム / Web System
AWS LambdaECS FargateSQSDynamoDBDatadog

A highly resilient serverless data processing pipeline utilizing AWS Lambda, SQS, ECS Fargate, and DynamoDB. Implements auto-scaling policies based on SQS queue depth with Datadog monitoring.

localhost:3000
aws-metrics-monitor LIVE STREAM
SQS Queue Depth124 Messages
Fargate Tasks Scale8 running / 10 max
Throughput
Proc:
Errors:
Lag:
infrastructure.yml
1version: "3.8"
2services:
3 data-processor:
4 image: internal-registry/processor:v1.2.0
5 deploy:
6 resources:
7 limits:
8 cpus: '0.50'
9 memory: 512M
10 reservations:
11 cpus: '0.25'
12 memory: 256M
13 environment:
14 - SQS_QUEUE_URL=https://sqs.us-east-1.amazonaws.com/12345/data-queue
15 - DYNAMODB_TABLE=processed-data-store
04

Zero-Trust Secure K8s Service Mesh

ă‚Šă‚§ăƒ–ă‚·ă‚čテム / Web System
IstioKubernetescert-managermTLSIngress

Implementation of a secure service mesh using Istio across multiple Kubernetes clusters. Features mTLS-by-default communication, fine-grained canary traffic routing, and secure ingress gateways via cert-manager.

localhost:3000
istio-security-meshmTLS: STRICT
Ingress GatewayHTTPS Router
‱‱‱‱🔒‱‱‱‱>
istio-proxyAuthenticated
Service A (v1)90% Traffic
Service A (Canary)10% Traffic
infrastructure.yml
1apiVersion: security.istio.io/v1beta1
2kind: PeerAuthentication
3metadata:
4 name: default
5 namespace: production
6spec:
7 mtls:
8 mode: STRICT
9---
10apiVersion: networking.istio.io/v1alpha3
11kind: Gateway
12metadata:
13 name: secure-gateway
14spec:
15 selector:
16 istio: ingressgateway
17 servers:
18 - port:
19 number: 443
20 name: https
21 protocol: HTTPS
22 tls:
23 mode: SIMPLE
24 credentialName: wildcard-cert
25 hosts:
26 - "*.harshitdev.ops"
HACKATHON ACHIEVEMENTS

HACKATHON VICTORIES

A curated log of first-place championships and podium finishes at regional and national engineering hackathons.
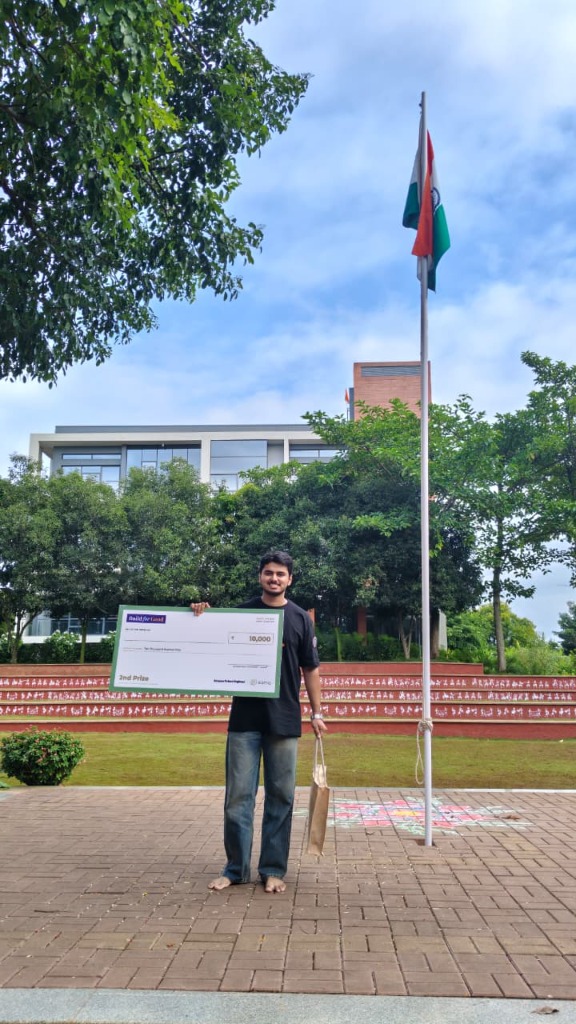
victory-monitor.sh
Build for Good Hackathon
SLIDE 1 OF 7
â–Č SYSTEM VICTORIES LOG
TOTAL: 7 CHAMPIONSHIPS● VERIFIED ONLINE

Workflow Pipeline

Technical Arsenal
Stage 1

Source & Build

c logocplusplus logotypescript logoreact logo
C/C++
TypeScript
React
Next.js
12s
Stage 2

Containerize

docker logolinux logognubash logo
Docker
Linux
Bash Scripting
45s
Stage 3

Infrastructure as Code

terraform logo
Terraform
AWS (EC2, S3, RDS, VPC)
EKS/ECS
2m 14s
Stage 4

CI/CD & Delivery

githubactions logogitlab logojenkins logo
GitHub Actions
GitLab CI
Jenkins
1m 30s
Stage 5

Observe & Monitor

prometheus logografana logozabbix logo
Prometheus
Grafana
Zabbix
CloudWatch
active

Get In Touch

連甥 / Contact

System Status

Real-time status of Harshit's core systems and APIs.

All Systems Normal
Problem Solving Engine
Operational
Coffee Levels
Degraded Performance
Willingness to Relocate
Operational
Current Deployment Pipeline
Idle - Ready for Hire
Last updated: Just now

TERMINAL RACER

DODGE THE DEV DEVILS ‱ SECURE THE PIPELINE
ARCADE STATE: READY

Use ← and → arrows to steer

Cabinet Steer Controller
â–Č SYSTEM DIAGNOSTICS SCREEN
● PIPELINE TRAFFIC LOAD
0OPS/SEC
HIGH SCORE:1,048 (HARSHIT)
PIPELINE SPEED:5 MB/s
DIFFICULTY:STABLE ROUTING
HOW TO PLAY:
Use keyboard ← and → arrow keys (or the glowing red/green arcade buttons) to dodge fatal system calls like Fork Bomb and rm -rf /. Build pipeline uptime for high scores!